Skip to content
Large projects · Security audits · PostgreSQL

Engineering that
survives year two
and can be proven.

We build platforms for operations that cannot stop, audit the security of systems that already exist with evidence you can check, and work PostgreSQL with the judgement of someone who sends patches to its core.

  • Contributions in PostgreSQL 19 author, reviewer and reporter in the core, with public commits
  • Isolation in the database enforced by PostgreSQL and audited for side channels
  • Findings with evidence severity, location and how to reproduce
  • Proof of optimality CP-SAT with a zero gap, not a heuristic

Operations copilot · ask it about your data

Fisios clinic · copilot panel demo with sample data
TÚ

—

—

—

source:

What we do

Three things. All three, with proof.

This page reads in a minute: we build large platforms, we audit the security of systems that already exist, and we work PostgreSQL from its core. Every line carries what backs it, and every proof can be checked.

  1. 01 Large projects

    Custom platforms for operations that cannot stop

    Healthcare, public procurement, certification: systems with thousands of documents inside, several clients who must never see each other, and people asking who touched what.

    • Architecture and data on PostgreSQL, with per-tenant isolation enforced in the database
    • Audit per transition from day one: who, when and what changed
    • AI that answers with its source, and optimisation with proof of optimality
    • Verified deployment, backups with tested restores and ticketed support

    The proof

    Five platforms in production under betrivasystems.com and some twenty applications running on AWS.

    How we work
  2. 02 Security audit

    A report that says what is right, what is not, and how it was proven

    Code, data, infrastructure and tenant isolation, reviewed with evidence. For systems that sign long contracts, go through tenders or hold third-party data.

    • A one-sentence verdict, findings by severity and what is missing as a programme
    • Every finding with its exact location and how to reproduce it
    • Side channels in tenant isolation (RLS), not just the policies
    • Mapped point by point to what the contract or tender demands

    The proof

    Method applied to a system under a twenty-year operating contract, plus our own security research on PostgreSQL.

    See the audit
  3. 03 PostgreSQL

    The engine, worked by someone who sends it patches

    Performance, isolation, migrations and extensions, with the judgement of someone who reviews and fixes the core on pgsql-hackers.

    • Seven accepted contributions in PostgreSQL 19: author, reviewer and reporter
    • Five extensions published on PGXN, pure SQL: they run on RDS, Aurora and Supabase
    • Co-maintainer of pg_isok and a patch of our own in the commitfest
    • SQL Server to PostgreSQL migrations done in production

    The proof

    Every commit linked to git.postgresql.org, on the PostgreSQL page.

    See the contributions

If what you need is none of the three, we say so in the first email.

After the demo

What the presentation never shows you

Every demo works. It is built with thirty records, one user and nobody in a hurry. You only get to know a system in month fourteen: thousands of records inside, two clients who must not see each other, and someone asking what happened in March.

Week 1

Search is instant

In the demo

You type three letters and the result is there. With forty records, anything is fast.

In production

With eighty thousand documents, that same search scans the whole table and takes eight seconds. People stop using it and go back to asking over WhatsApp.

What prevents it

Indexes and vector search defined in the initial data model. Not a late optimisation: it is how the table was designed on day one.
Month 6

The second client arrives

In the demo

The platform still looks just as good. You add the new organisation and everything keeps working.

In production

One query that forgot the client filter returns the other organisation's data. Nobody notices — until somebody notices.

What prevents it

Isolation enforced by the database rather than by the programmer: if the query forgets the filter, the row still does not show up.

Month 14

"Who opened this record in March?"

In the demo

That question never comes up in a demo.

In production

The audit, the complaint or the lawsuit arrives, and the answer is "I don't know". There is no record, because it was never written.

What prevents it

An audit log from the very first state transition. It costs little to write at the start and cannot be reconstructed afterwards.

What cannot be done later

Scaling later is expensive. Auditing backwards is impossible.

Almost everything can be fixed by paying: migrate the database, rewrite the module, buy a bigger machine. History cannot. If the audit log was not written on day one, those years do not exist and no budget will bring them back. The same goes for data stored wrong or never stored at all. That is why these decisions are made at the start: not because they get expensive later, but because some of them can no longer be made at all.

Isolation

Two clients, one platform, zero rows crossing over

Almost all multi-client software separates data in code: a filter on an identifier that someone has to remember to write in every single query. It only takes forgetting once, in one query, on a Tuesday. Here the filter does not live in the code: PostgreSQL enforces it. Switch the session identity and watch the same query.

Active session

The query being run — identical in both cases

SELECT id, name, reason
  FROM patients
 ORDER BY id;
id patient
1042 Sample patient A
1043 Sample patient B
1044 Sample patient C

3 rows returned

The policy that enforces it

ALTER TABLE patients ENABLE ROW LEVEL SECURITY;
ALTER TABLE patients FORCE  ROW LEVEL SECURITY;

CREATE POLICY tenant_isolated ON patients
  USING (tenant_id = current_setting('app.tenant_id', true)::uuid);

-- The context is set PER TRANSACTION (third argument: true).
-- When the connection returns to the pool, the tenant goes with it.
SELECT set_config('app.tenant_id', $1, true);
Context of this session 8f2c1a7e-…-norte

Sample data; the mechanism is the one running in production. Two details you only notice once someone has been burned: FORCE also applies to the table owner, and a transaction-local context stops a pooled connection from dragging the previous tenant along.

Operations

Shipping is the start. Afterwards, we stay.

A system in production is a system with someone behind it: monitoring, incidents with a ticket number, verified deployments and backups that actually restore. This is what it looks like from the inside.

Operations console · betrivasystems.com sample view live --:--:--
Health per service · last 48 h operational degraded down
EIR Doctores Fisios Licitaciones CertiCore PostgreSQL nginx · TLS
−48 h −24 h now
99.97 %
30-day availability
184 ms
p95 response
4 min
last restore
0
open incidents

How every delivery is validated

  1. 01 Tests against the real database Integration, not simulations: isolation and transitions tested where they will run.
  2. 02 Deployment with verification Atomic swap and a response check before anything is called done.
  3. 03 Backups with a tested restore A backup counts once it has been restored, with date and duration.
  4. 04 Audit per transition Who, when and exactly what changed, from day one.
  5. 05 Ticketed support, online Every incident with a number, an owner and a traceable answer.

Products

Five systems, five real operations

01 Oncology · Radiotherapy

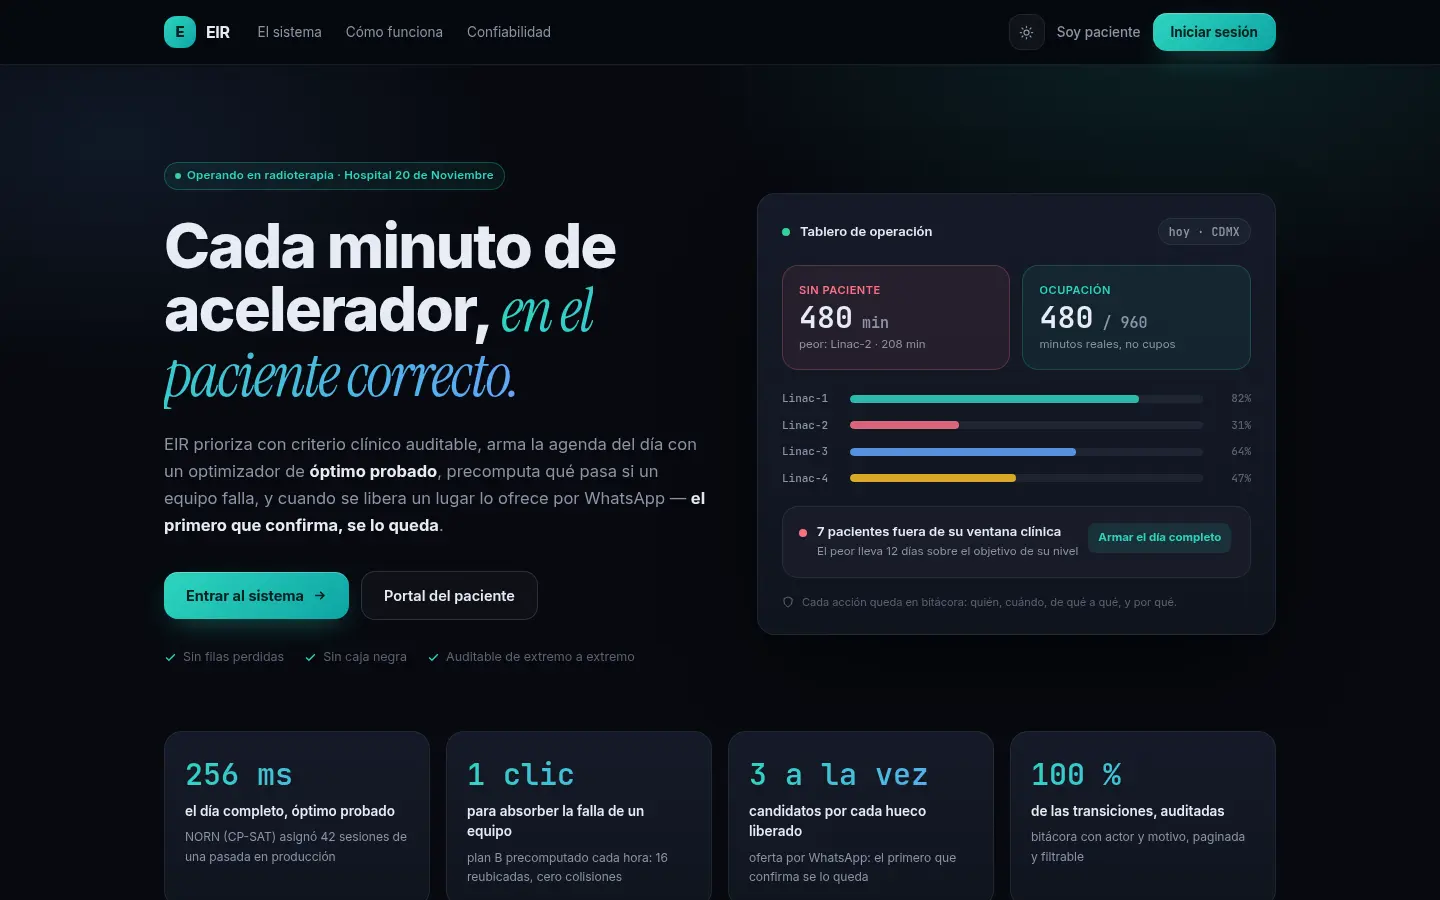
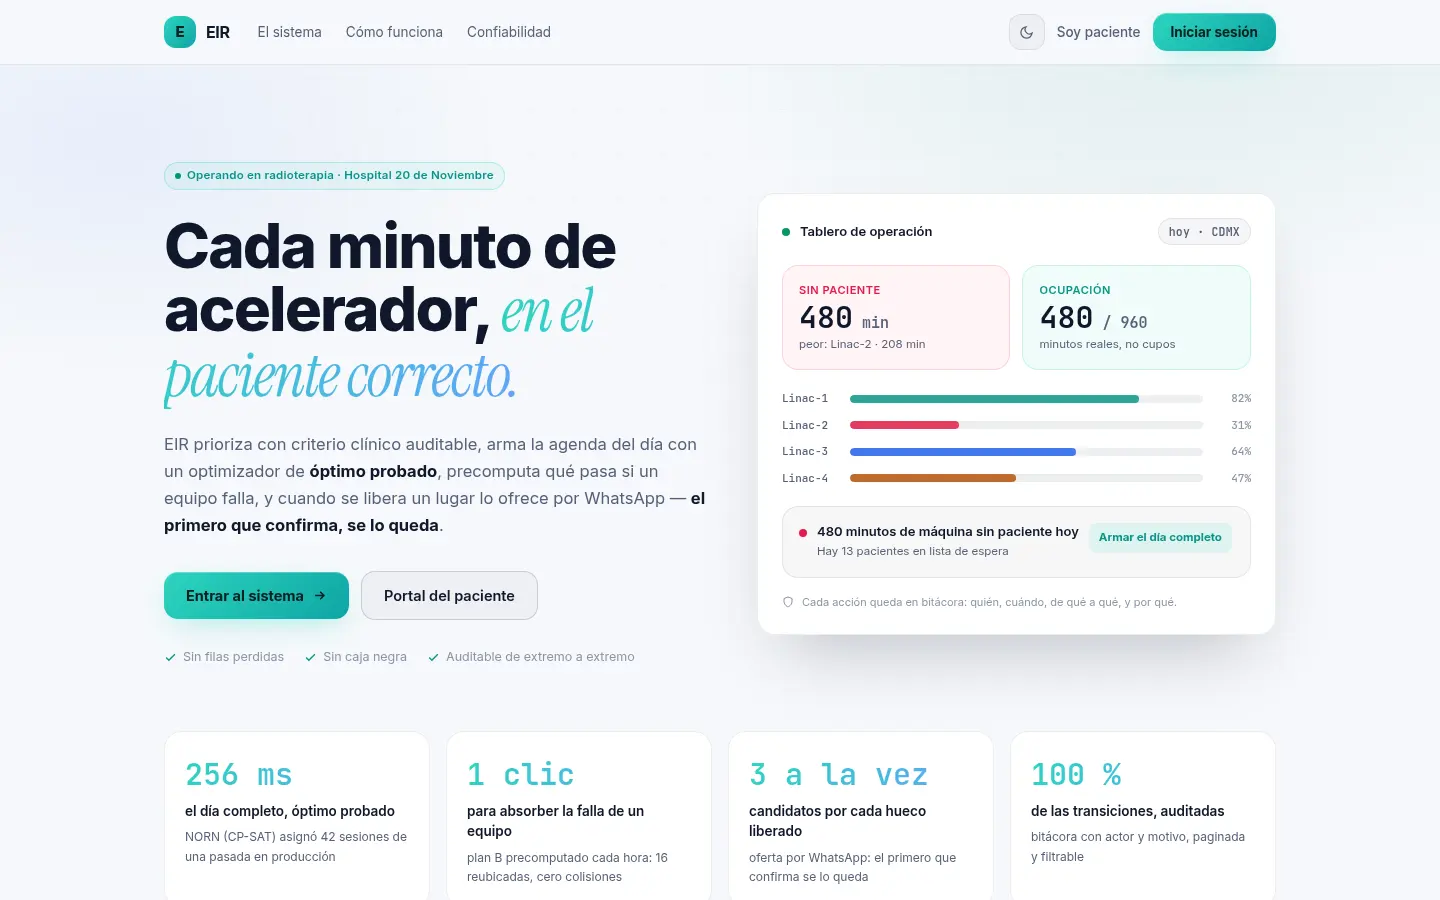
EIR

Intelligent scheduling for radiotherapy

Patient scheduling, multichannel notification and end-to-end traceability for a radiotherapy department. Treatment continuity is the rule that wins: the engine proposes the order, the oncologist signs the clinical category.

  • Lexicographic clinical priority (emergency / urgent / routine)
  • Machine downtime rescheduled in minutes, not phone calls
  • Audit trail on every state transition
Visit the site
eir.betrivasystems.com
EIR — Intelligent scheduling for radiotherapy EIR — Intelligent scheduling for radiotherapy
02 Private practice

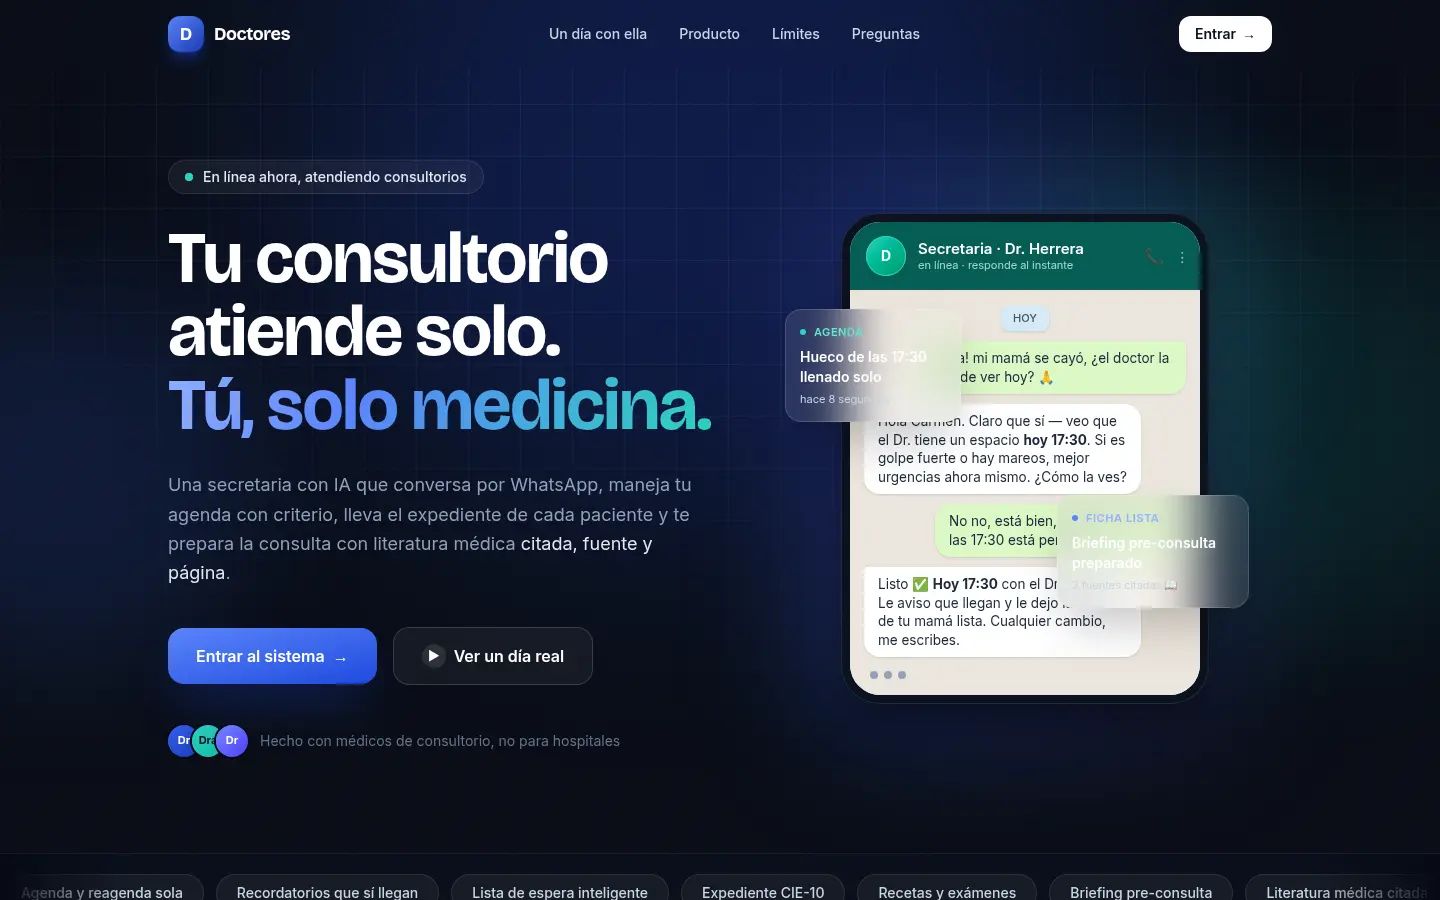
Doctores

The receptionist your practice never had

A WhatsApp virtual receptionist, a traceable clinical record and cited medical knowledge. Built for the doctor running their own practice, not for the hospital with an IT department.

  • Scheduling and confirmations over WhatsApp — no app to install
  • Clinical record with an auditable history
  • Medical answers always carry their source
Visit the site
doctores.betrivasystems.com
Doctores — The receptionist your practice never had
03 Physiotherapy clinic

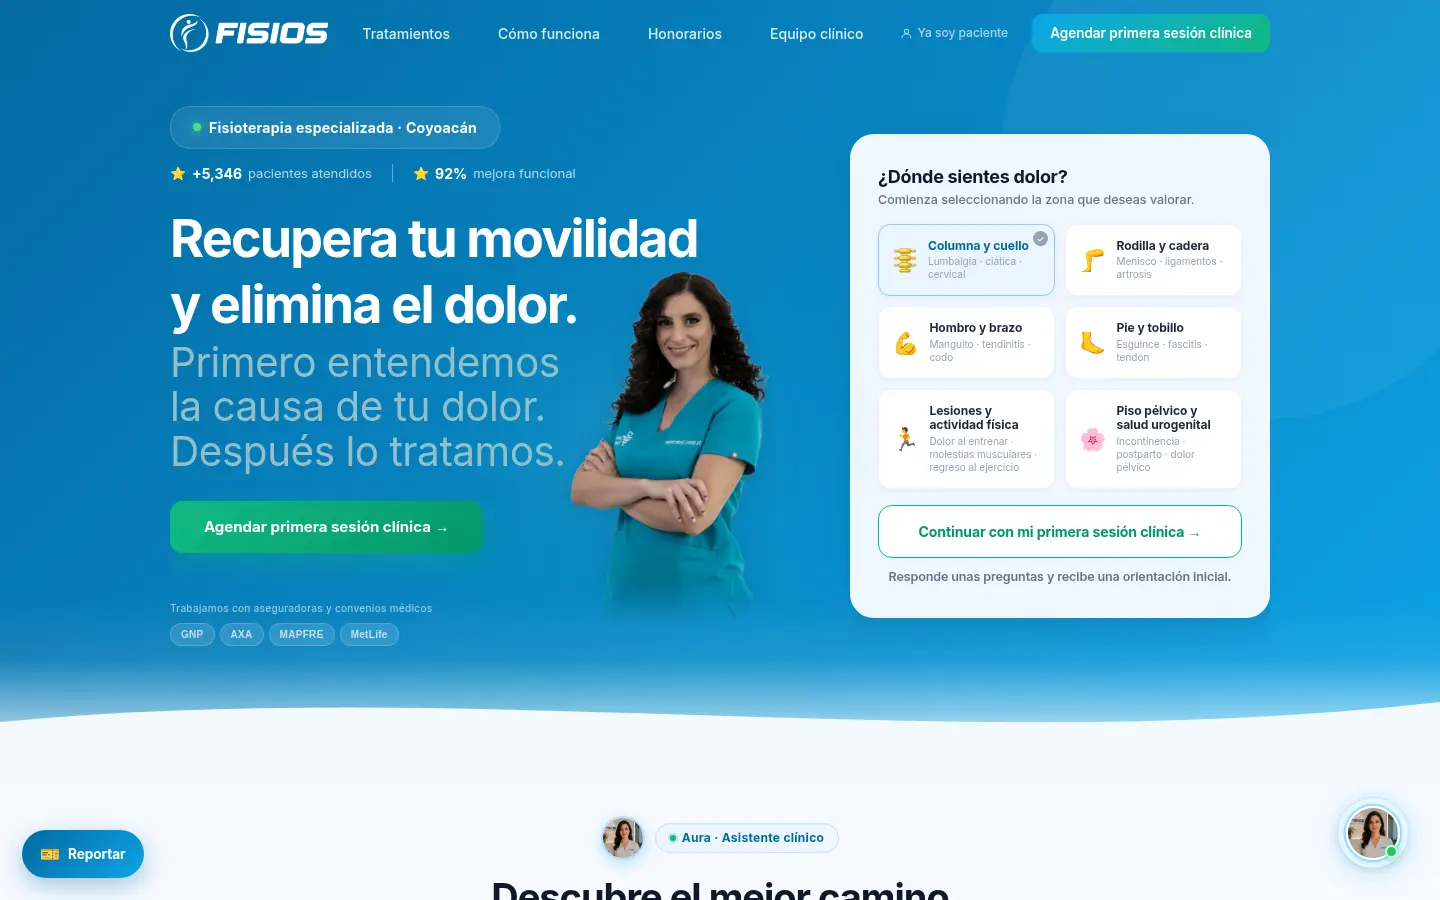
Fisios

Full physiotherapy care, booked online

Website and platform for a real clinic in Coyoacán, Mexico City: guided assessment, online booking and treatment follow-up. The full case of an operation that sees patients every day.

  • Online booking wired into the clinic’s daily operation
  • Per-patient progress notes
  • Public site tuned for local search
Visit the site
fisios.betrivasystems.com
Fisios — Full physiotherapy care, booked online
04 Public procurement

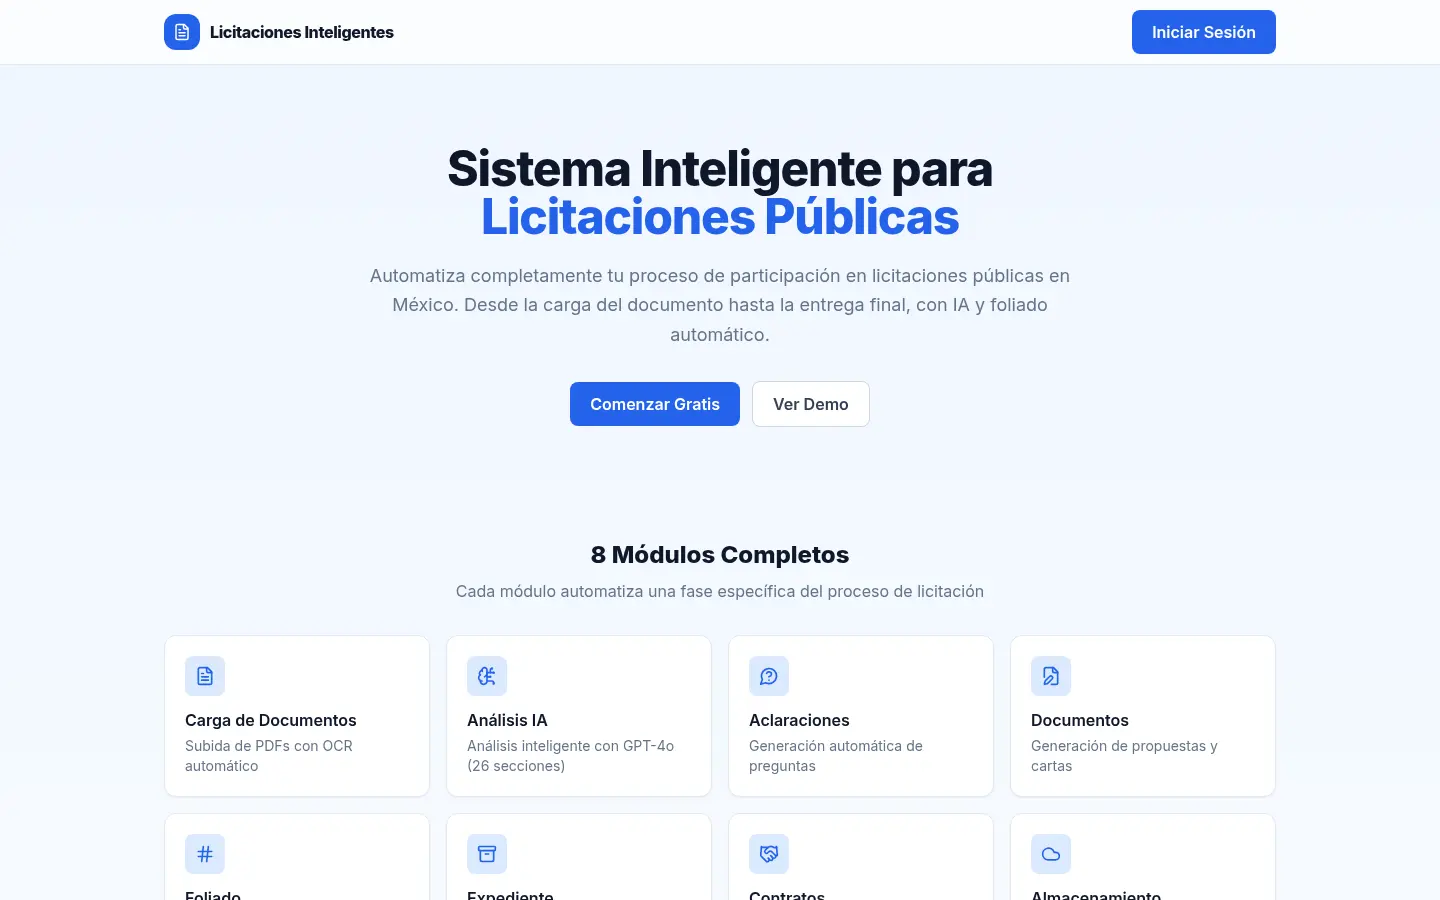
Licitaciones Inteligentes

AI-assisted tender analysis

Assisted reading of public tenders: terms, annexes and deadlines turned into a clear bid / no-bid decision, with the source document always in view.

  • Requirements and deadlines extracted from the tender documents
  • Opportunity screening against the company profile
  • Every conclusion linked to the paragraph backing it
Visit the site
licitaciones.betrivasystems.com
Licitaciones Inteligentes — AI-assisted tender analysis
05 Competency certification

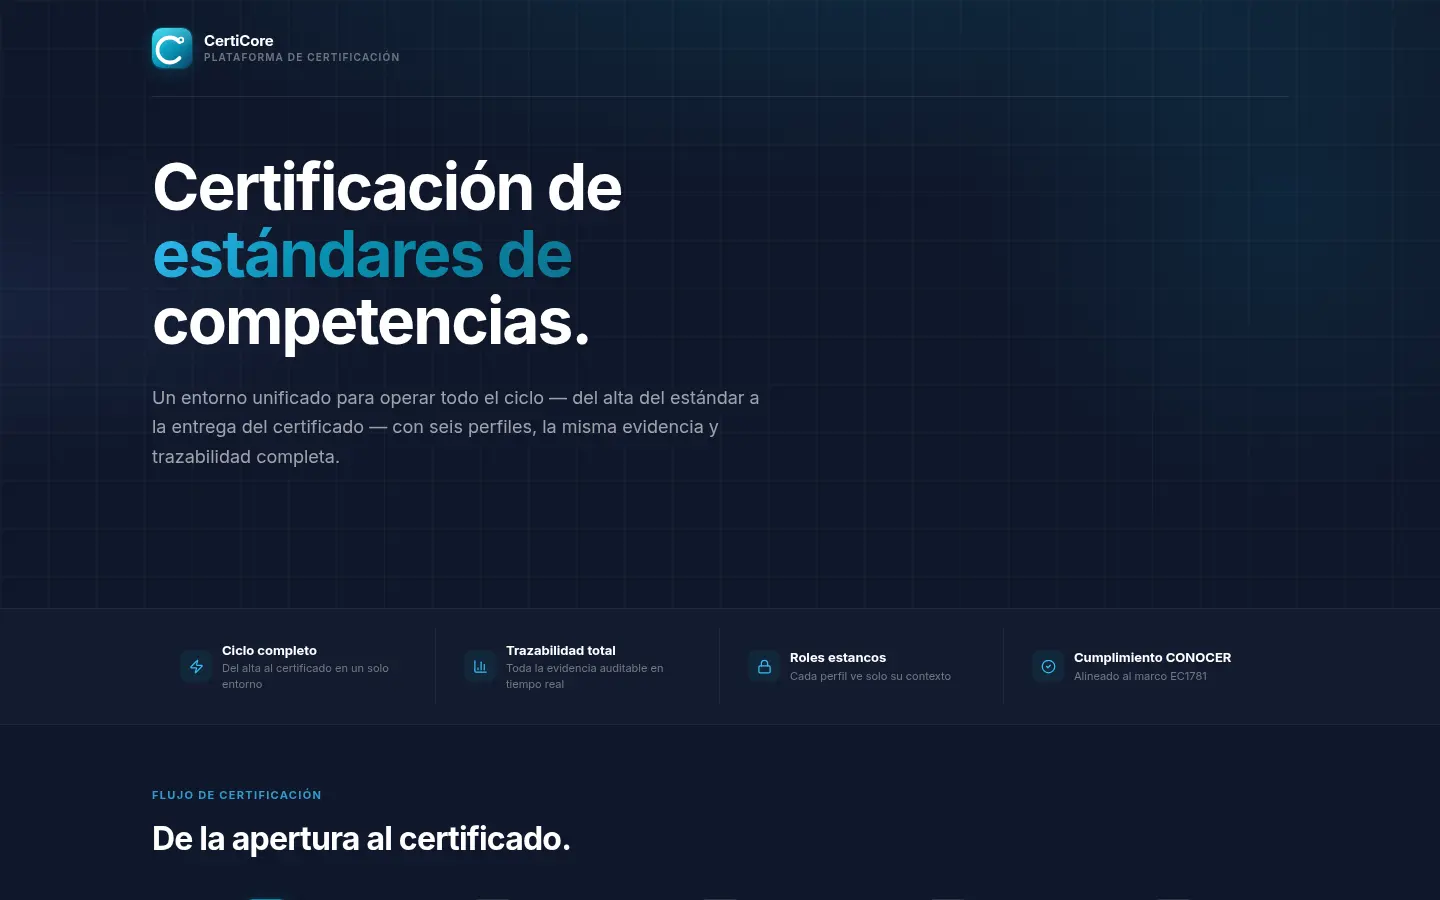
CertiCore

Standards, assessment and certification in one place

A unified platform for standards management, assessment and CONOCER certification: from course to evidence, and from evidence to a verifiable certificate.

  • Full path: standard → course → assessment → certificate
  • AI-assisted evidence review for the assessor
  • Certificates with folio, QR and public verification
Visit the site
certicore.betrivasystems.com
CertiCore — Standards, assessment and certification in one place

Criteria

The checklist you should be judging us by

These are the decisions that get made once and are not reversed afterwards. They work for evaluating us and for evaluating anyone else. Take it to your next meeting: if the vendor answers with a demo instead of a fact, you have already learned something important.

Technical evaluation checklist · software vendors

Betriva Systems · free to use · no sign-up, no email

0/7

  1. Why it matters It is the most expensive failure and the quietest one: by the time it is found, it has already happened.

    The answer that should worry you

    "We filter by client ID on every query."

    Ours

    Row Level Security in PostgreSQL, with FORCE enabled and a transaction-local context. Demonstrated live, further up this very page.

  2. Why it matters A backup that has never been restored is not a backup: it is a file with good intentions.

    The answer that should worry you

    "We have automatic daily backups."

    Ours

    A tested restore, with its date and how long it took. A backup with no restore test does not count as a backup for us.

  3. Why it matters A model will confidently write a deadline that does not exist. And it gets signed anyway.

    The answer that should worry you

    "It uses state-of-the-art artificial intelligence."

    Ours

    Every statement linked to the document, the page and the paragraph. If the system cannot show the source, it does not answer.

  4. Why it matters It is what the auditor, the complaint or the lawsuit asks for. And it cannot be reconstructed backwards.

    The answer that should worry you

    "We store the last modified date."

    Ours

    A log per state transition: who, when, from where and exactly what changed. Written from day one.

  5. Why it matters It determines whether you can change vendors or whether the vendor owns your operation.

    The answer that should worry you

    "We take care of all that, don't worry about it."

    Ours

    All of it in the client's name. We could walk away tomorrow and nothing would fall over — which is exactly the point.

  6. Why it matters An entire operation hanging off a third party's API is a business risk, not a technical one.

    The answer that should worry you

    "That is very unlikely to happen."

    Ours

    Critical flows run on local models, on our hardware or the client's. As a bonus, sensitive data never leaves either.

  7. Why it matters Between a reasonable solution and the optimal one there are machine hours and money, every month.

    The answer that should worry you

    "The algorithm looks for the best available combination."

    Ours

    CP-SAT and QUBO models returning the optimum along with its gap. When the gap is zero, no better schedule exists and it can be proven.

If your current vendor cannot answer one of these, it does not mean the system is bad today. It means the bill arrives later.

Contact

Got a process falling apart on you?

Tell us which operation you want to put in order. If we can help, we say so with a plan and a timeline; if it is not our thing, we say that too.

Write to us at contacto@betrivasystems.com · We reply within one business day.